Vibecode Rescue: speel.co
- Asking
- $500,000
- Revenue
- $0/mo
- Offers
- 27
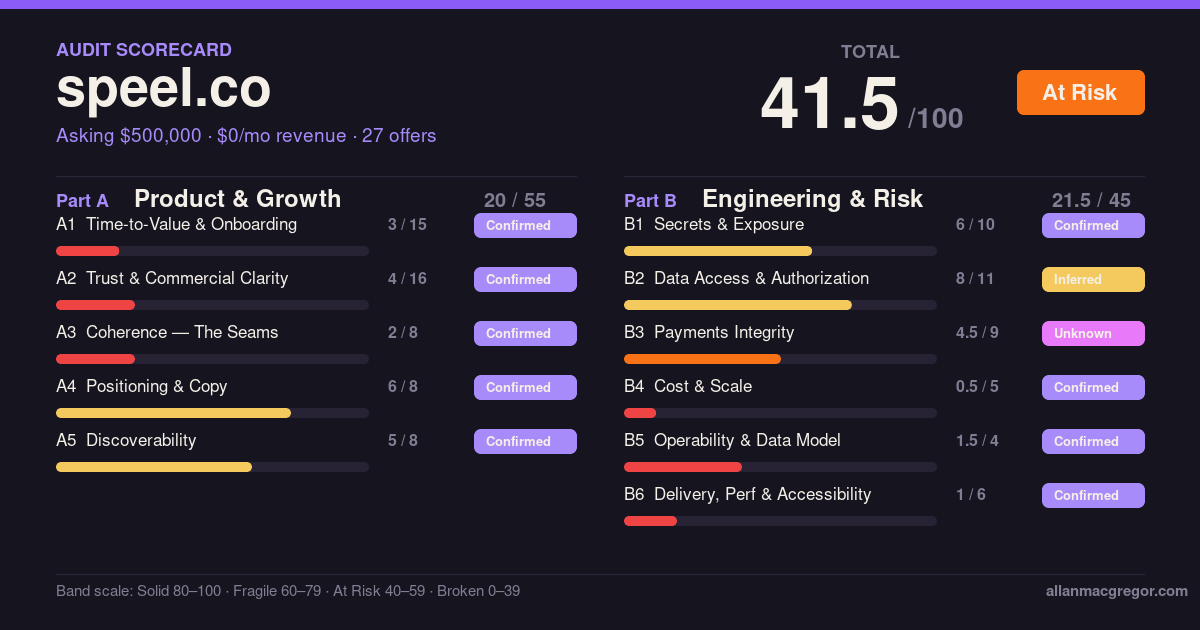
An AI ad-creative tool listed at half a million dollars with no revenue and 27 offers. 41.5/100 — At Risk. The legal documents live on a different domain, and the free trial charges you a dollar.
speel.co generates AI avatar ad creative — UGC-style video ads without filming anything. It reports no revenue, the asking price is $500,000, and twenty-seven people have made offers against 22,275 views.
It scored 41.5 out of 100. At Risk.
Observed on 2026-08-04 against a snapshot of the page, the shipped bundle, response headers, DNS and the legal pages. Signup and onboarding were walked through on a real account.
The product runs on a different domain than the one it advertises
The listing is for speel.co. Sign in with Google and the consent screen says something else:
Sign in to speel.app Review speel.app's Privacy Policy and Terms of Service to understand how speel.app will process and protect your data.
The privacy policy and terms of service both live at speel.app/terms-privacy. Both domains sit on the same Cloudflare nameservers and resolve to the same address, so this is one operator running two names. The effect on a user is that the thing they signed into, the entity processing their data, and the terms binding them are all on a domain the marketing never mentions.
Meanwhile speel.co's own legal routes are worse than missing:
$ curl -o /dev/null -w '%{http_code}\n' https://speel.co/privacy
200
$ curl -o /dev/null -w '%{http_code}\n' https://speel.co/terms
200
Both return 200. Both render the login page. So do /privacy-policy and /terms-of-service. Any automated check that verifies "does this domain serve a privacy policy" passes, and a person clicking through finds a password field.
The free trial costs a dollar
The FAQ on speel.co, verbatim:
"Speel offers a one-time free trial that lets you explore the platform and its features. The trial includes 90 credits, which allows you to create 1 video and up to 5 images, giving you full access to see how Speel works for your needs. The trial is not time-limited, your credits remain valid until they are fully used. There is no automatic renewal…"
The onboarding flow offers plans at $35, $79 and $129 a month, and underneath: "Not ready to commit? Start with a free trial →".
That link goes to a checkout reading "Explore Speel for $1", total due today CA$1.43, requiring card number, expiry, CVC, name and billing address, processed by Whop.
A dollar is not much money. The problem is the word. The product's own FAQ describes a paid trial as free, and the answer runs four sentences past the point where the price should have appeared. Whop is not named anywhere on speel.co either, so the first time a user learns who is taking their card details is at the moment of taking them.
You cannot see the product without paying
That is A1, and it is the reason this scores where it does. The product offers a demo to nobody. Sample output stays behind the login, and reaching the product requires entering payment details first.
That is the conversion funnel, not a pricing decision. Every prospective customer is asked to pay before they are shown anything, and the product reports no revenue.
What it gets right
- Positioning is the strongest part of the property. The plans differentiate on concrete numbers — 55 versus 123 versus 200 videos a month, named models, workspace seats — rather than adjectives. Pricing is fully visible before signup.
- The onboarding flow itself is clean. Google OAuth, workspace creation, plan selection, each step landing where it should.
- HSTS is set at two years.
- Clean credential scan across nine classes, with no placeholders or builder artifacts in the bundle.
- Cancel anytime is stated on every plan.
- Server-rendered marketing HTML, so there is something for search engines to read.
The engineering underneath
Five of six security headers are missing. CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy are all absent; HSTS alone is present.
The domain publishes no SPF record, so anyone can send mail as @speel.co, and DMARC sits at p=none, which monitors and blocks nothing.
Mobile Lighthouse: performance 33, a 10.7-second largest contentful paint, 11.8 MB transferred across 156 requests. Accessibility 88, with 31 elements failing contrast and five links carrying no discernible name.
A request for a path that does not exist returns HTTP 200 with the app shell — a soft 404.
One thing worth asking about
The web archive holds 37 captures of speel.co going back to 2011-05-01. The product is recent; the domain is not. That is common and usually harmless — someone bought an aged domain — but it means "founded" dates and any traffic history attached to this name deserve a question rather than an assumption.
The score
What I'd fix first
-
Make speel.co's
/privacyand/termsserve the policy, or redirect to speel.app. A login form at those URLs defeats every automated check that a 404 would have caught. - Stop calling a $1 trial free. Change the FAQ or change the price. The current wording is the kind of thing that ends up in a chargeback.
- Name Whop as the payment processor before the checkout screen.
-
Publish an SPF record and move DMARC off
p=none. - Add the five missing security headers, and let someone see the product before they pay.
Disclosure
Findings went to the operator before this published. These audits are free and public; the paid version is a Code Health Check, and the rescue work after it is Track 03 on my services page.
